Default Groups & Permission Sets
Every organization is created with a set of predefined groups and matching permission sets that cover the most common roles. They are a good starting point and can be assigned to your users as-is. For the underlying concepts see the Permission System overview.
| The predefined groups and permission sets are system-managed. They cannot be edited or deleted, and they are required for a correct access-control model. You can, however, freely create your own groups and permission sets alongside them. |
Predefined Roles
Each predefined role exists both as a permission set (defining what it may do) and as a group (whose members receive it). In the Portal, the group name is prefixed with your organization’s unique name in capital letters, written below as ORGA. For an organization named "Blue Corp" that prefix is BLUECORP, so the group appears as BLUECORP Administrator.
| Group (in the Portal) | Permission Set | Grants |
|---|---|---|
ORGA Administrator |
Administrator |
Full access to all features of the organization, including users, user groups, permission sets, organization settings and the license. This is the superuser role for an organization. |
ORGA IOT Manager |
IOT Manager |
Full access to devices and their provisioning, configurations, buildings, networks, sensor data and actuators, automations, alerts, statistics and the organization settings. Does not include the administration of users and permissions. |
ORGA Device Manager |
Device Manager |
Full access to devices and everything belonging to them: device provisioning, configurations, device groups, device actions, automations, alerts, statistics and the device-related settings. Does not include buildings or the administration of users and permissions. |
ORGA User |
User |
Read access to the data of the organization: devices, configurations, buildings, sensor data, statistics, automations and alerts. Also allows controlling actuators and managing the personal profile and access tokens. This is the baseline role for regular members. |
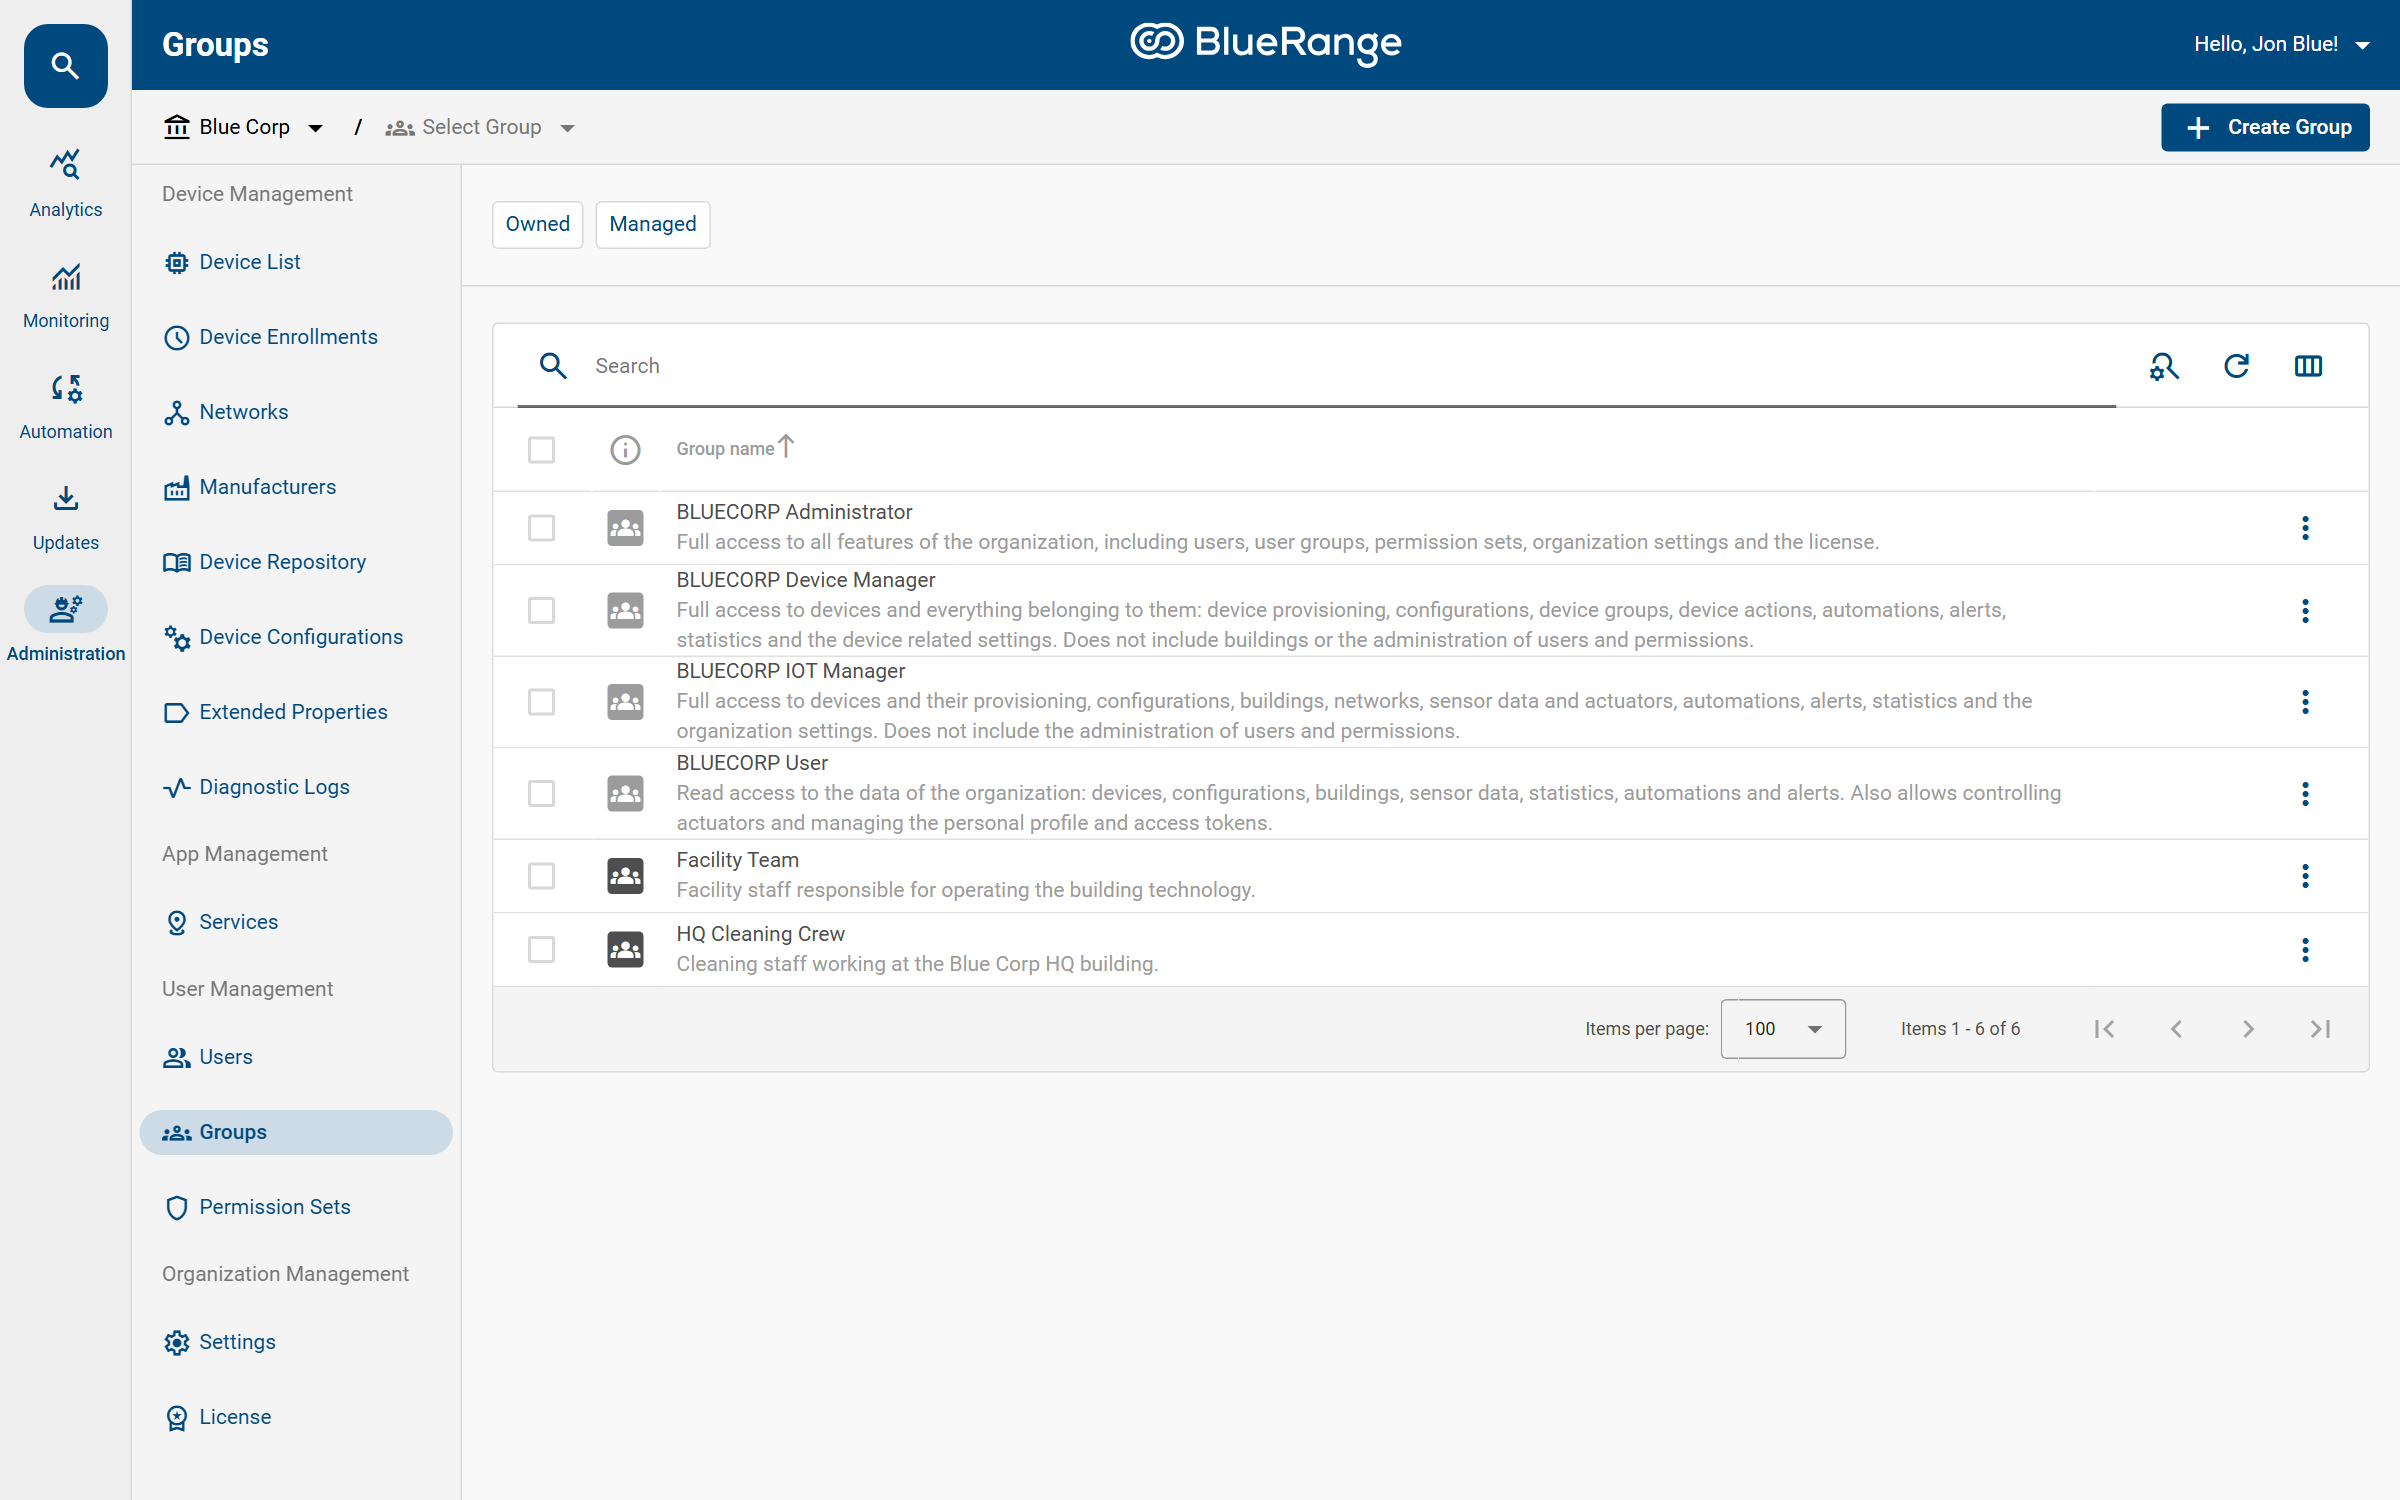
| The predefined Administrator group is a member of the other system groups, so an administrator automatically inherits their permissions. |
Building on the Defaults
-
Need a role the defaults do not cover? Create a custom Permission Set. The Create Permission Set dialog even offers templates such as Commissioning Engineer, Facility Manager or Employee as a starting point.
-
Want the same access for a whole team? Create a Group, assign the permission set to it and add your users.
-
Want a role that applies to only certain buildings or devices? Combine it with Partial Permissions.
System Administrator
In addition to the per-organization roles above, on-premise and dedicated cloud installations have a global System Administrator in a dedicated ADMIN group of the system organization. A System Administrator manages all organizations and their users, but does not take part in the day-to-day IoT features of an individual organization. See Setting up Organizations for details.